

SIEM Monitored 24x7 by a SOC: Costly Compliance Gaps for Indian BFSI Firms
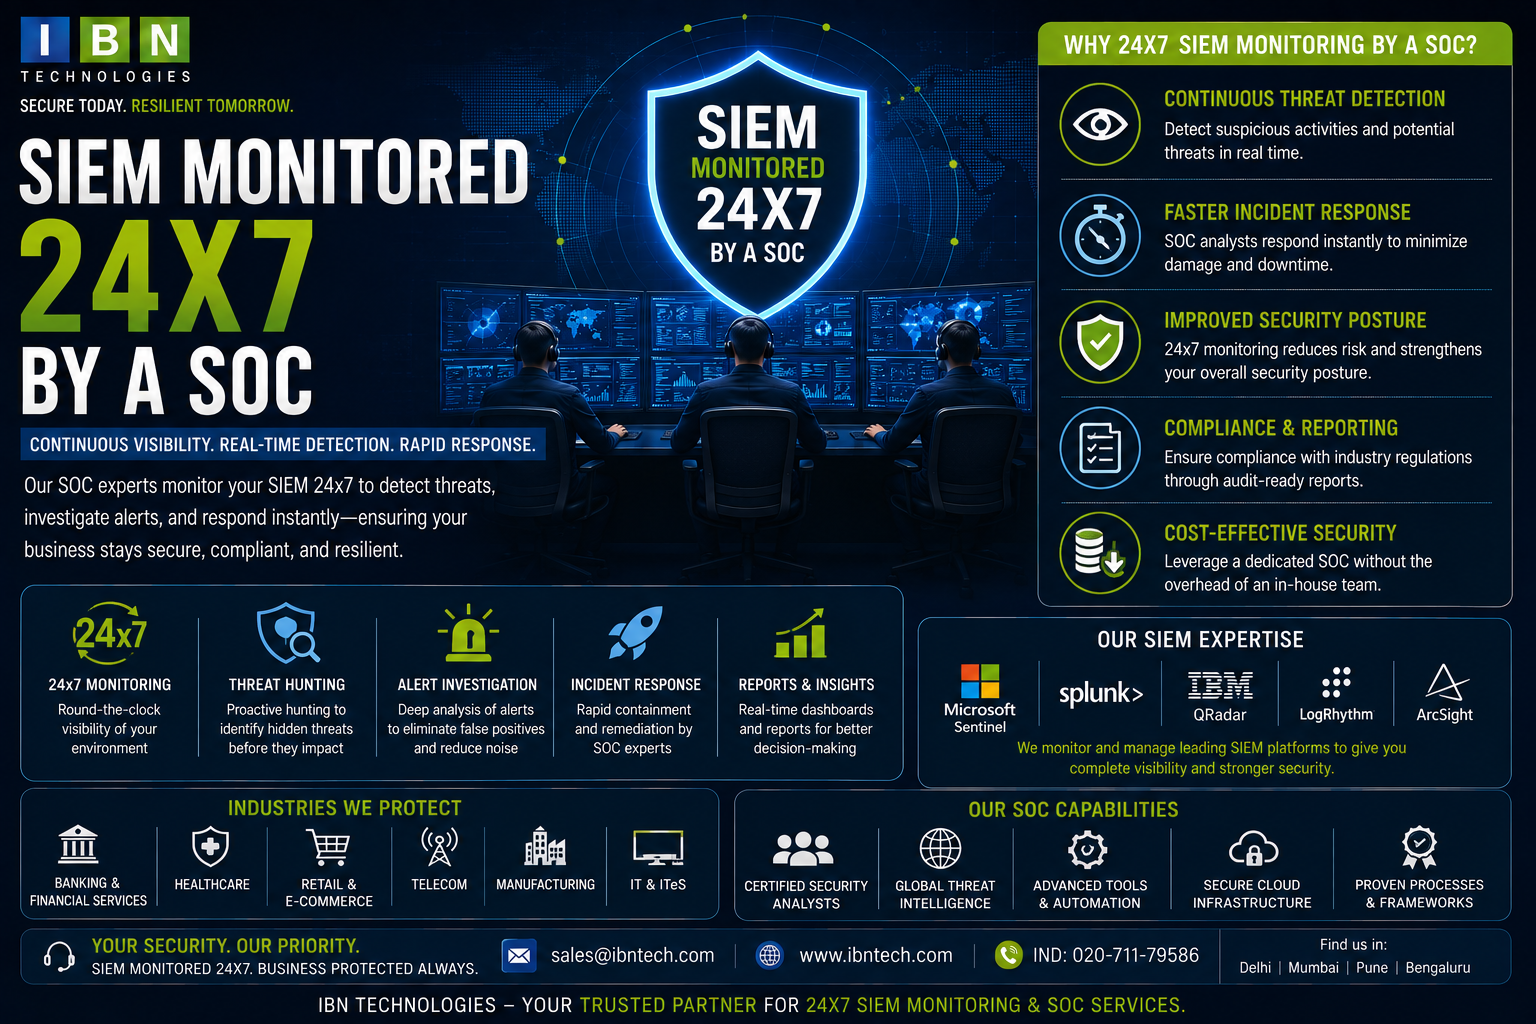
SIEM Monitored 24x7 by a SOC: Strengthening Security and Compliance for Indian BFSI
Financial institutions operate in an environment where security incidents can have consequences far beyond technology disruption. siem monitored 24x7 by a soc combines centralized security-event visibility with continuous monitoring and human analysis, helping BFSI organizations maintain a more consistent approach to threat detection, investigation, and security reporting.
For Indian BFSI businesses, this model can be particularly relevant when security operations must support both day-to-day risk management and broader governance requirements.
Why Compliance Reporting Needs More Than Security Tools
A security platform can generate logs and alerts, but compliance-oriented security operations require more than collecting information.
Organizations need to understand what is happening across their technology environment, determine which events require investigation, maintain appropriate records, and demonstrate that security processes are being managed consistently.
This creates an important distinction between having security data and being able to use that data effectively.
A SOC can provide the operational layer required to monitor relevant events, investigate suspicious activity, escalate incidents, and organize information for reporting. When SIEM capabilities are integrated into this process, security data from multiple sources can be brought together for analysis.
For BFSI organizations, that combination can help connect security operations with governance rather than treating compliance as a separate documentation exercise.
How Managed SOC Providers with Compliance Reporting Support BFSI Operations
For organizations evaluating managed soc providers with compliance reporting, the reporting capability should be considered alongside monitoring and incident-handling processes.
A managed SOC can continuously monitor security events while producing structured information about incidents, alerts, trends, and other security activities. This can give internal security and governance teams a clearer view of what is being monitored and how significant events are handled.
The reporting layer becomes especially useful when management needs a summarized view of security activity rather than raw event data.
However, reporting should reflect actual monitoring operations. A report is most valuable when it is connected to meaningful detection, investigation, escalation, and response processes.
Why In-House Monitoring Can Become Difficult at Scale
BFSI organizations often have complex technology environments. Security events can originate from endpoints, networks, servers, applications, identity systems, cloud environments, and security devices.
An internal security team may understand the organization's infrastructure extremely well, but continuous monitoring requires sustained analyst availability and specialized operational processes.
The challenge becomes more pronounced when alerts arrive outside standard working hours. A security event does not become less important because the relevant team is unavailable.
Building a full internal SOC can address some of these challenges, but it also requires people, processes, technology, management, and ongoing operational investment.
A managed SOC offers another model: the organization retains its internal governance and technology responsibilities while an external security operation provides continuous monitoring and specialist analysis.
What Makes Compliance-Oriented SOC Monitoring Effective?
BFSI decision-makers should evaluate a SOC according to how well security operations, reporting, and governance work together.
Important considerations include:
- Monitoring scope: Identify which infrastructure, applications, endpoints, and security devices are included.
- Continuous coverage: Confirm that monitoring operates around the clock.
- Alert investigation: Understand how analysts assess suspicious events and determine their significance.
- Incident escalation: Establish how serious findings are communicated to designated stakeholders.
- Reporting depth: Determine whether reports provide useful information for security and management review.
- Evidence handling: Clarify how relevant monitoring and incident information is maintained.
- Detection improvement: Ask how recurring findings and emerging threats influence monitoring practices.
- Integration: Check whether the service can work with the organization's existing security environment.
A strong SOC should help turn security information into operational knowledge that decision-makers can actually use.
The Value of Continuous Monitoring for BFSI
Continuous monitoring provides an important advantage: security visibility does not stop when an office closes.
A suspicious authentication event, unusual network behavior, or potentially compromised endpoint can be reviewed when it occurs rather than waiting for a scheduled security check.
This can support faster awareness of potential incidents and reduce the likelihood that important events remain unattended for extended periods.
There is also a governance benefit. Security teams can use monitoring information to identify recurring patterns, evaluate the effectiveness of controls, and communicate relevant trends to leadership.
For BFSI organizations, this creates a stronger connection between cybersecurity operations and enterprise risk management.
A Banking and Financial Services Scenario
Consider a financial services organization with employees, applications, servers, cloud resources, and network infrastructure generating security events throughout the day.
An account associated with privileged access produces an unusual sequence of authentication events. A single event may not provide enough information to determine whether there is a security problem.
The SIEM can correlate related activity from relevant sources. SOC analysts can then investigate the sequence and determine whether it warrants escalation.
If the event becomes a confirmed or suspected security incident, the organization's established response process can be activated. The resulting activity can also contribute to appropriate internal reporting and security records.
The important point is that monitoring, investigation, escalation, and reporting form one connected operational cycle.
Compliance Reporting Should Not Become a Paper Exercise
One risk for organizations is treating compliance reporting as something performed only before an audit.
That approach can encourage teams to gather information retrospectively instead of maintaining useful security records as part of normal operations.
A continuously monitored environment provides an opportunity to make reporting part of the regular security lifecycle.
Security teams can review trends, investigate important events, identify recurring issues, and maintain relevant operational information throughout the year.
This can make management reviews more meaningful because decision-makers are not relying solely on a snapshot prepared for an external assessment.
IBN Technologies offers managed SIEM and SOC capabilities that include 24x7 security monitoring, threat detection, incident response, threat intelligence, security-device monitoring, dashboards, and compliance-oriented reporting.
Organizations should still evaluate their specific regulatory and contractual obligations independently. A managed SOC can support compliance activities, but it does not by itself make an organization compliant.
Questions to Ask Before Selecting a Provider
A BFSI organization should look beyond a provider's monitoring-hour claim and examine the complete operating model.
- Which security sources can be monitored?
- How are alerts prioritized?
- Who investigates suspicious events?
- How are critical incidents escalated?
- What reporting is available to security leadership?
- How are recurring incidents identified?
- Can the service support cloud, hybrid, and on-premises environments?
- How does the provider communicate significant security findings?
- Can reporting be aligned with internal governance requirements?
These questions help organizations assess whether a service can become part of their security operation rather than simply supplying another monitoring dashboard.
Building Compliance Readiness Into Everyday Security
Compliance readiness is stronger when security practices are consistent throughout the year.
BFSI organizations can improve this foundation by clearly defining monitoring responsibilities, maintaining appropriate escalation procedures, regularly reviewing detection quality, documenting significant incidents, and ensuring that security reporting reflects operational reality.
A SOC can support these activities by providing continuous oversight and structured security information.
The internal organization remains responsible for governance decisions, risk acceptance, regulatory interpretation, and broader security controls. The SOC's role is to provide the monitoring and operational support that helps those decisions rest on timely security information.
Moving From Visibility to Security Accountability
For Indian BFSI organizations, security monitoring increasingly needs to serve two purposes at once: identifying potential threats and providing dependable operational visibility.
A SIEM monitored continuously by a SOC can help bridge that gap. Instead of collecting security events and reviewing them only when convenient, organizations can establish an ongoing process for detection, investigation, escalation, and reporting.
That model can also make conversations between security teams, technology leaders, and management more productive. Rather than discussing cybersecurity entirely in technical terms, organizations can use monitoring trends and incident information to understand where attention is required.
The result is a security operation that supports both immediate threat awareness and longer-term governance.
For BFSI organizations evaluating their security maturity, siem monitored 24x7 by a soc is therefore not simply a technology configuration. It represents an operating approach in which security information is continuously observed, investigated, and translated into actionable intelligence. When supported by appropriate reporting and governance processes, it can help Indian financial organizations build a more consistent and accountable approach to security operations.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - [email protected]

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)